
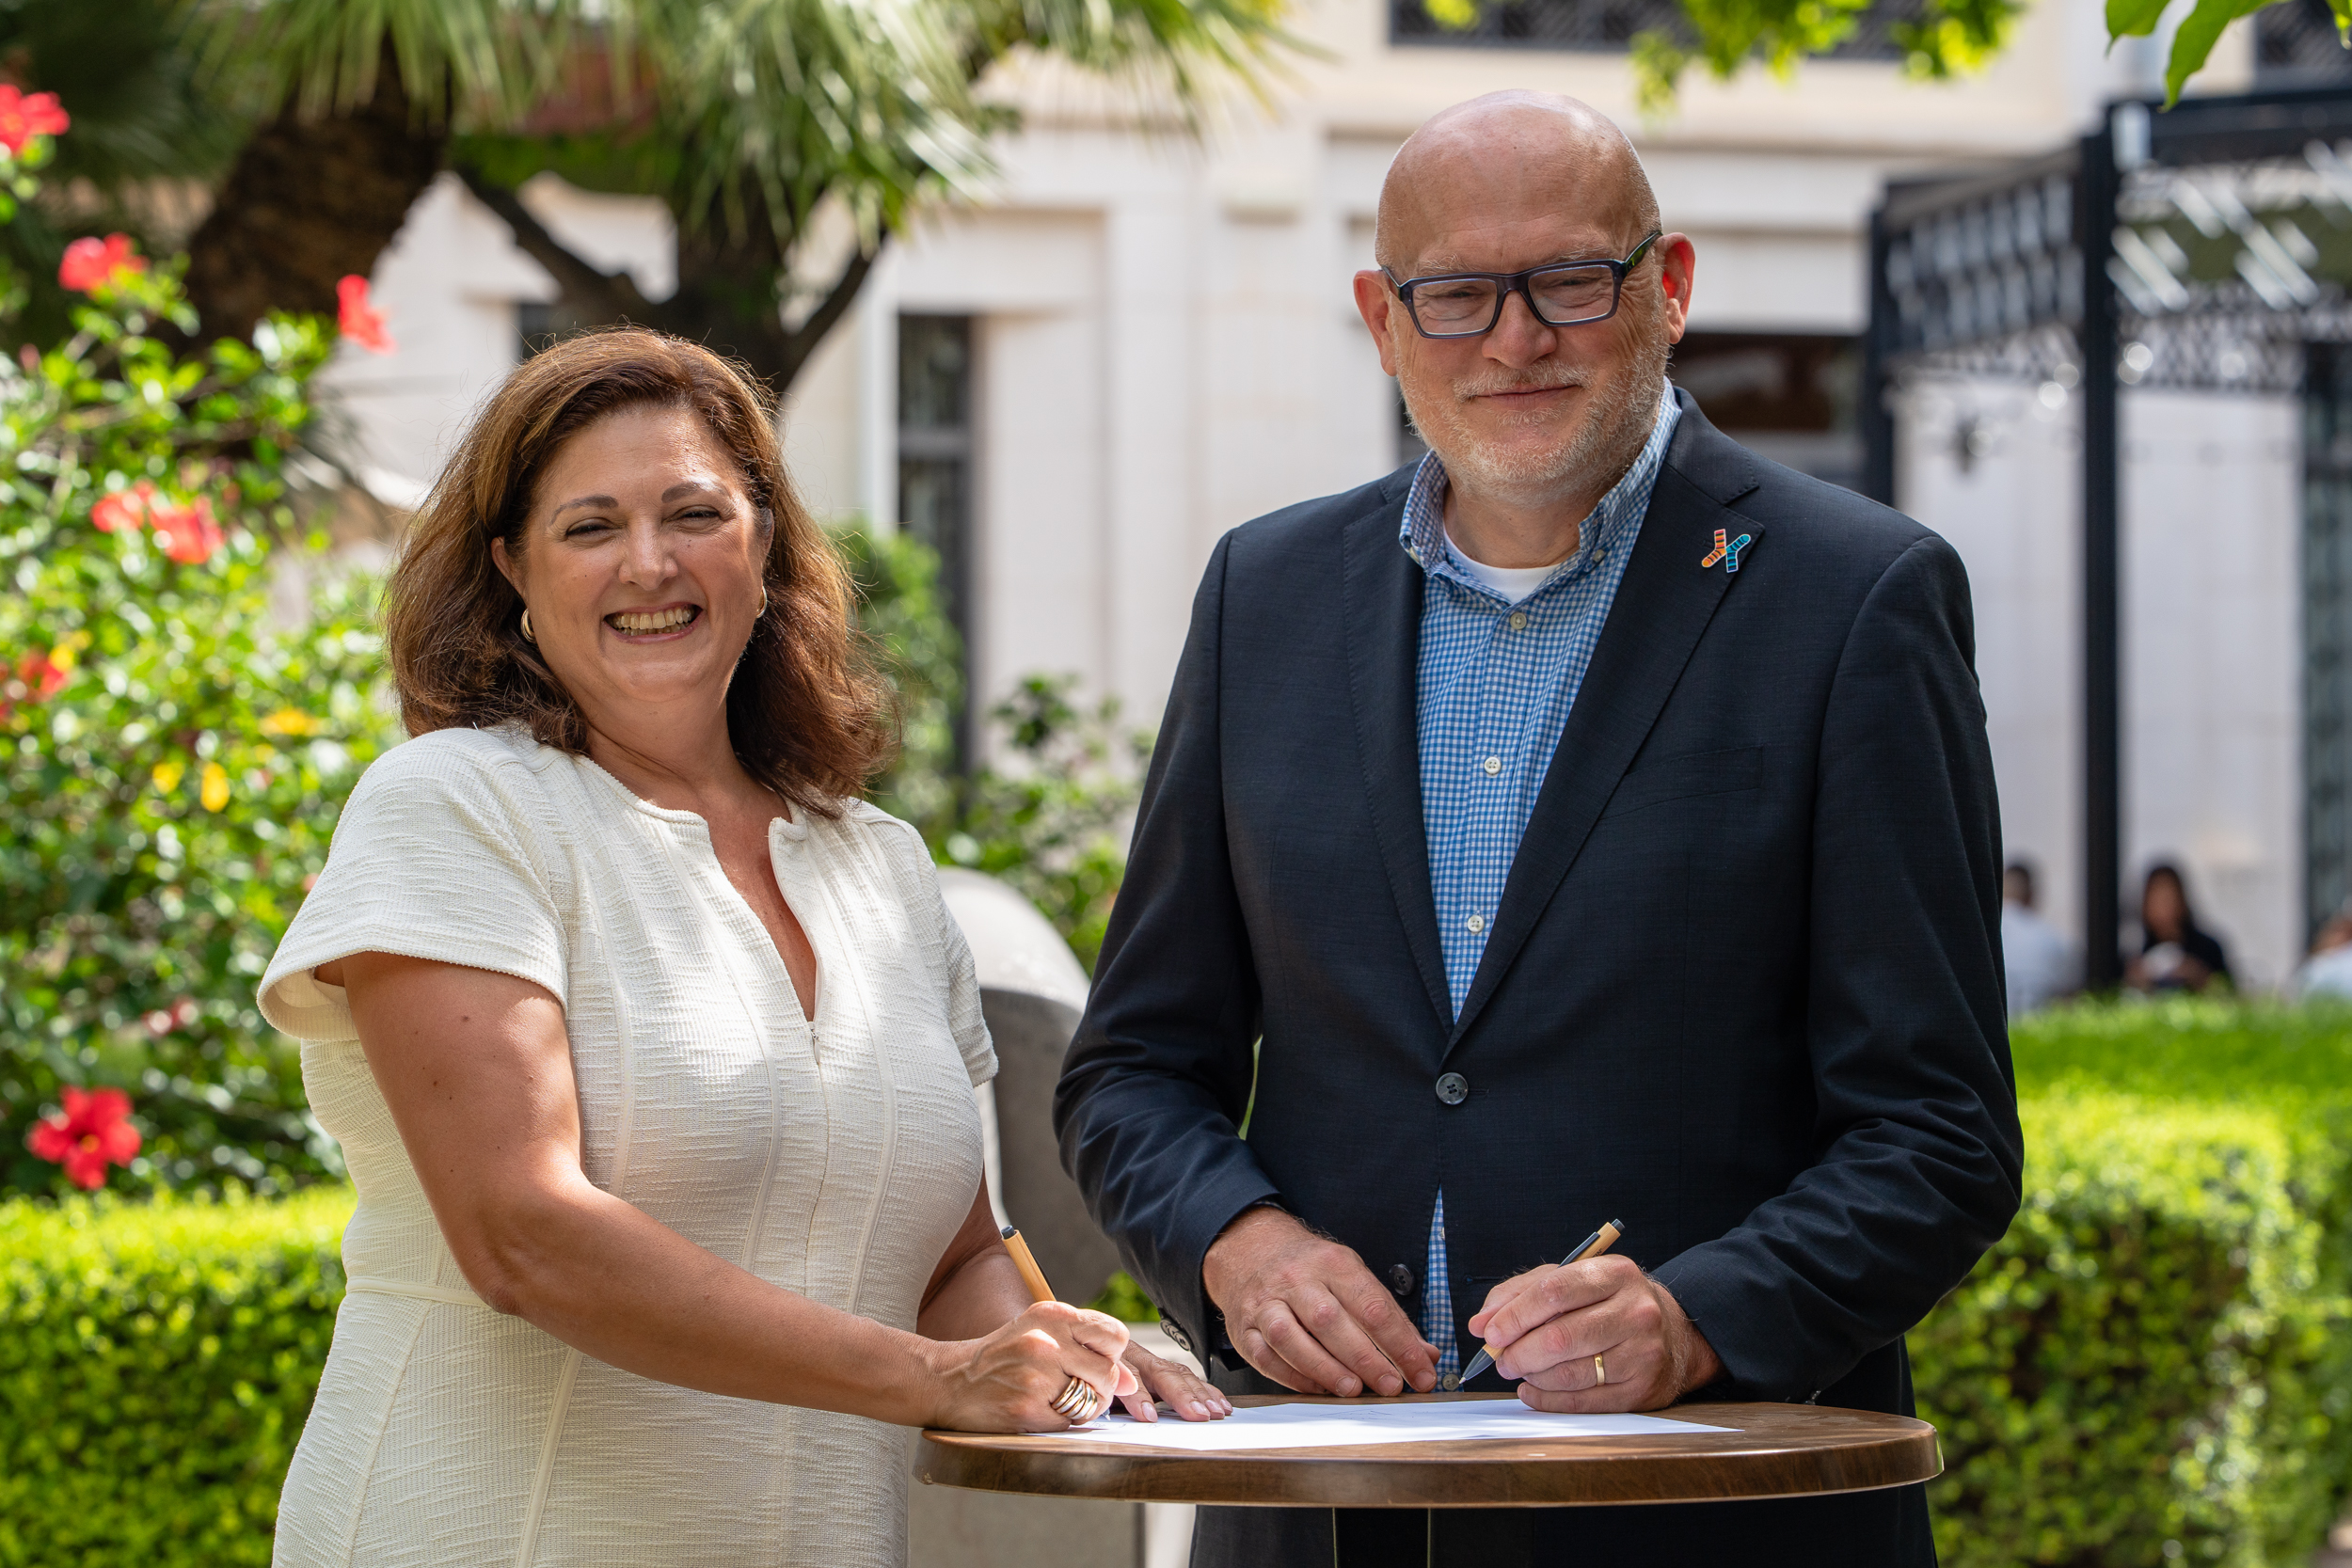
As container shipping continues to digitalise, securing the container release process remains a key challenge for carriers, terminals and logistics providers. With interoperability, cybersecurity and industry-wide standardisation increasingly in focus, Antonia Saratsopoulou, Managing Editor at Container News, spoke with Nico Wauters, CEO of T-Mining, about the vulnerabilities of current container release processes, the shift away from PIN codes, and the challenges of establishing a secure and interoperable global standard.
1. Container release processes still vary considerably between ports, terminals and carriers. From a security perspective, where are the most significant vulnerabilities in the current container release process?
Container release in ports has long been a risky process in international maritime logistics. As processes differ widely across ports and terminals, a fragmented landscape has developed over the years, causing not only operational friction and delays, but also posing major security risks. Pincodes in particular are a big cause for concern. Europol identifies PIN codes as a primary vector for European drug cartels.
In the past, when someone sent an email containing the PIN code for a container to another company in the supply chain, that email with the code naturally stayed right there in your mailbox under ‘Sent Items.’ So that isn’t really a transfer; it’s a copy. Eventually, twenty to thirty people end up seeing that PIN code. Billions invested in physical surveillance are bypassed daily by a simple code in an unencrypted message.
Our customers are worried about their personnel being threatened or bribed by organized crime gangs. Additionally, criminal networks and drug cartels use intercepted PIN codes to steal high-value cargo or pick up containers loaded with illegal drugs in major European ports.
2. The industry is moving towards common standards for Secure Container Release. What elements of the process need to be standardised to enable different carriers, terminals and technology providers to operate securely and interoperable?
Secure, interoperable container release is an important enabler of the industry’s digital transformation. I believe there are a few key elements that need to happen to enable this:
- The process must transition from PIN codes (that are not secure) to a unified standard. A digital token standard will enable the containers to be released only by the authorized party. Secure Container Release (SCR) for example replaces PIN codes with digital tokens. Like a relay baton, the digital right to collect a container can only be held by one party at a time.
- Seamless interoperability is needed. This is only possible via Open APIs. Integration via standardised API layers are absolutely crucial so that the ERP systems from the carriers, the FMS for freight forwarders, the TMS for transport companies, the Terminal Operating Systems (TOS) and the Port Community Systems (PCS) can exchange information smoothly without the need for custom patch work integrations at each port.
- Industry-wide alignment with organizations like the Digital Container Shipping Association (DCSA / DCSA+) is also crucial. DCSA can help ensure global uniformity across ocean carriers, ports, terminals, forwarders, and technology providers.
3. To what extent can weaknesses in container release procedures contribute to cargo theft and fraud? As release processes become increasingly digital, is there also a risk that vulnerabilities simply shift from physical procedures to digital systems?
The current PIN code dependent container release procedures pose a significant risk for cargo loss and fraudulent pickups. Drug cartels attempt to bribe individuals holding the code (frequently through threats and intimidation) in order to gain access to the container.
Even with the process becoming ‘digital’ there is still a big risk, organized crime networks exploit digital blind spots through various ways. For instance, in 2025, Greek police arrested six port employees at the Port of Piraeus for smuggling cocaine. There have been multiple other instances across Europe, and this demonstrates the persistent thread of workforce corruption and the exploitation of port logistics for organised crime.
Additionally, we must not forget that PIN codes sent via emails may be ‘digital’ but they are still unsafe, if the personnel is at risk of being threatened or bribed. With AI this risk becomes more pertinent. It goes without saying that a more digital process will be challenged in different ways such as hacking. Cyber security becomes more important than ever before.
4. Greater interoperability requires different systems and stakeholders to exchange information. What new cybersecurity or data-security risks could this introduce, and how can these risks be addressed?
- Cybersecurity and Data Security Risks: Broad data exchange introduces risks of data hacking, identity theft, targeted cyberattacks on centralized data repositories (“honeypots”), and the exposure of sensitive commercial relationships between supply chain partners.
- Addressing Risks via Peer-to-Peer Privacy: These security risks are addressed using a decentralized Peer-to-Peer (P2P) architecture where data is exchanged exclusively between direct connections, eliminating central honeypots and concealing non-adjacent connections to protect commercial privacy.
- Cryptographic Identity Wallets: Security is further enforced through cloud or user-hosted ID Wallets using cryptographic key authentication, ensuring that only invited, verified organizations can receive or transfer release tokens.
5. Ports and terminals operate with very different levels of digital maturity, often using established or legacy systems. How can a common Secure Container Release standard be implemented without requiring organisations to replace their existing technology infrastructure?
I don’t see the need for reinventing the wheel or introducing a new system. When ports or terminals evaluate container release options, building a custom in-house solution may be explored. But it will take years of development, ongoing TOS maintenance overhead and will generate pushback from carriers & shippers confronted with yet another solution.
Dispatchers today would be better served by a Transportation Management System (TMS) that integrates directly with slot booking and cargo release platforms, allowing their software to automate these processes. For this you don’t need a central system provided by one port operator, but easy ways to integrate e.g. through standardized interfaces where all parties continue to use their existing software but they are linked via an API to a decentral release system.
In my opinion, the only central system for the transporter should be their own ERP hence the TMS, for freight forwarders the FMS, for the terminals the TOS. Carriers such as Hapag-Lloyd and MSC integrate SCR into their own digital products via APIs.
Using SCR for example, also helps ports because standardizing on a sector-wide solution taps directly into an established major carrier network (including players like MSC, Hapag-Lloyd, and CMA CGM) sparing them the heavy lifting of convincing carriers to adopt local, isolated platforms
These systems, serving single enterprises, are interconnected with many private solution providers and multiple public platforms interconnecting them with the outside world like an enterprise router is your gateway to the internet.
6. One of the biggest challenges for any global digital standard is widespread adoption. How can Secure Container Release standards be made practical not only for major carriers and large terminals, but also for smaller operators and markets with less-developed digital infrastructure?
Over 8000+ logistics companies across 25 countries in Europe already use SCR to release their containers.
Adoption at this scale has been possible due to two main reasons:
- Due to an active commitment from top ocean carriers (such as MSC, Hapag-Lloyd, and CMA CGM) as well as implementations in Belgian terminals such as MPET in Antwerp and Port of Limburg in Genk. With these implementations across regions we have ensured the safe handover of millions of containers in the last 10 years.
- The low friction setup of the SCR web app that enables even small operators with 2 trucks to use the platform. The web app is a low entry solution for small operators where you only need a PC with an internet connection. Larger players, on the other hand, prefer connecting their software via an API integration.
Since 2016, we’ve gained first-hand experience implementing Secure Container Release with leading carriers and terminals around the world. Our partnership with DCSA allows us to bring those practical insights into the development of a global standard. A standard like the one DCSA aims to bring will help shape solutions that are practical and interoperable across the industry.
7. From your experience with existing Secure Container Release implementations, what are the main technical, operational or organisational barriers that still need to be overcome before a common standard can achieve widespread adoption across the container shipping industry?
- Ecosystem Onboarding Inertia: Overcoming operational resistance to change and managing the administrative task of onboarding, inviting, and connecting tens of thousands of hauliers, subcontractors, and forwarders across global supply chains.
- Fragmented Regulatory Jurisdictions: Dealing with varying national regulations across jurisdictions, which creates regulatory arbitrage that organized crime networks exploit.
- Diverse Digital Readiness: Adapting to varying IT infrastructure capabilities across global regions while maintaining backward compatibility during phased transitions.
- Long Enterprise Adoption Cycles: Managing the inherently long sales and evaluation cycles of major global ocean carriers, which requires patient capital and structured alignment through industry standards organizations like DCSA.